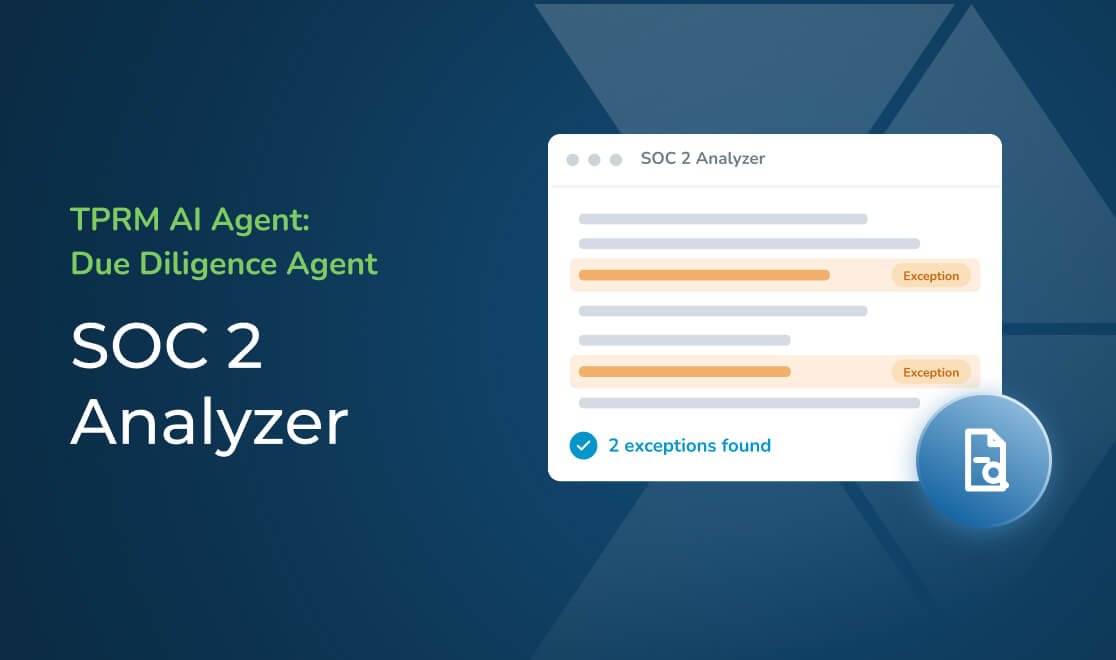
TPRM AI Agent: SOC 2 Analyzer
SOC 2 reports can run 80 to 120 pages long, with critical details often buried beyond the opinion letter. Under queue pressure, analysts may miss exceptions, complementary user entity controls, and other findings that affect your organization’s obligations.
Integrating NIST CSF into Third-Party Risk Management: Strategies for Enhanced Security and Compliance
Use Software to Follow OCC 2023-17 Interagency Risk Guidance
The Federal Reserve, Federal Deposit Insurance Corporation (FDIC), and the Office of the Comptroller of the Currency (OCC) have issued new third-party risk management (TPRM) guidance, OCC 2023-17, to help banking organizations manage third-party risk. This interagency TPRM guidance supersedes the previous OCC guidance on managing third-party relationships, OCC 2013-29, and provides principles that organizations […]
The SEC Cybersecurity Rule and the CISO’s Pivotal Role
When the government perceives those entrusted to its care are in danger, it takes action— case in point: the seatbelt law. Since the 1970s, the National Highway Traffic Safety Administration (NHTSA) has lobbied for passive restraint systems to protect drivers and passengers in the event of a crash. Though controversial when the rules were first […]
How ISO 27002 Prepares You for Cybersecurity Certifications
ISO 27002 is a powerful tool to demonstrate your information security commitments to customers, investors and regulators. Because it focuses on the development and maintenance of a strong information security management system (ISMS), this certification prepares you to achieve other cybersecurity certifications, both by driving you to collect your policies into a single system and […]