Featured Resources
ProcessUnity State of Third-Party Risk Assessments 2026
Content Library
ProcessUnity Earns ISO/IEC 42001:2023 Certification for Responsible, Human-Guided AI in Third-Party Risk Management
Independent certification from DEKRA validates how ProcessUnity governs the AI behind ProcessUnity Risk Index, giving customers confidence in the AI that powers their TPRM programs. Concord, MA — October 14, 2026 — ProcessUnity, the Third-Party Risk Management (TPRM) company, today announced it has received certification to ISO/IEC 42001:2023 Artificial Intelligence Management System, the international standard […]
Vendor Risk Analysis: How to Prioritize High-Risk Vendors (Without the Guesswork)
In our inherent risk series, we’ve explored what an inherent risk rating is and how to build an effective vendor risk tiering model. But once that baseline is established, a new question emerges: Which high-risk vendors require attention first? It’s a pressing question. ProcessUnity’s State of Third-Party Risk Assessments 2026 report found that organizations assess […]
TPRM AI Agent: Issue Remediator
Writing clear remediation instructions takes time. When language varies by analyst or leaves requirements open to interpretation, vendors may challenge the request instead of addressing the issue, further delaying remediation and leaving issues unresolved.
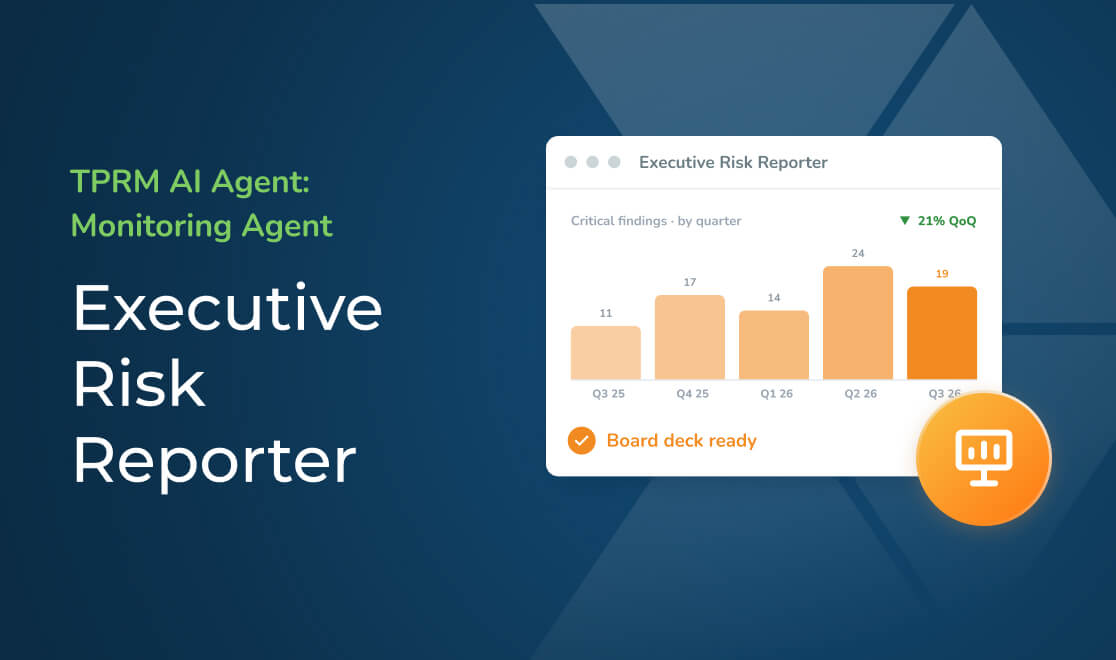
TPRM AI Agent: Executive Risk Reporter
When leadership asks for a clear view of vendor risk, it can take analysts hours to assemble information from a sprawling record. Inconsistent formats and narratives make it difficult to compare vendors or present a coherent picture of portfolio risk.
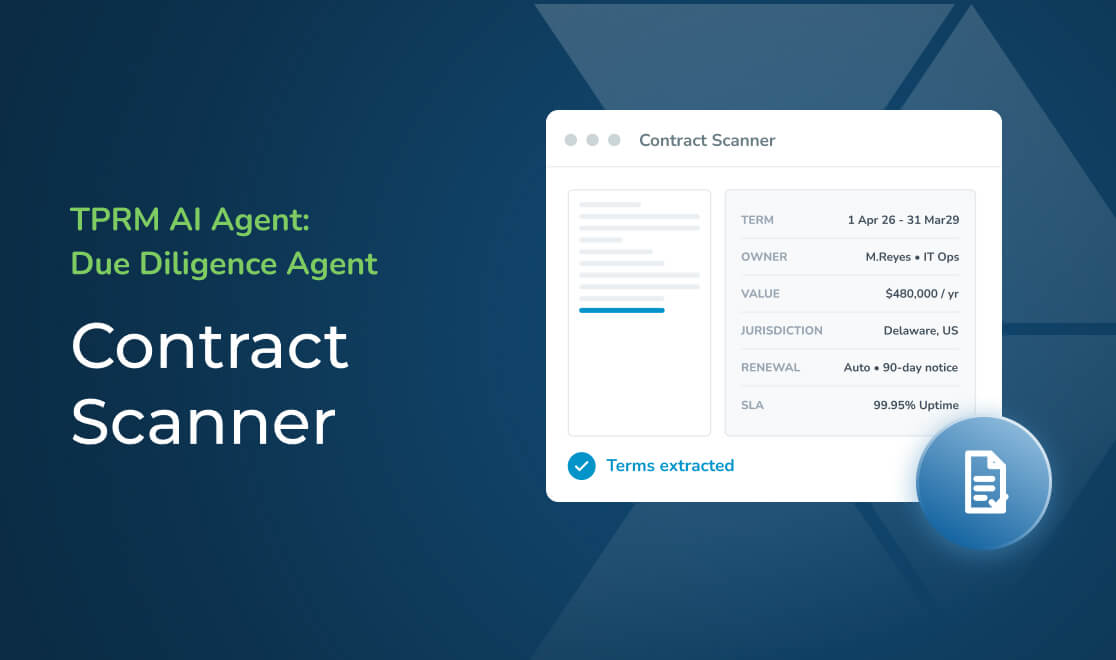
TPRM AI Agent: Contract Scanner
Executed contracts often span dozens of pages, with critical terms scattered throughout the agreement. When dates, renewal conditions, service levels, and other details are retyped manually, information gets missed, vendor records remain incomplete, and renewal windows can close unnoticed.
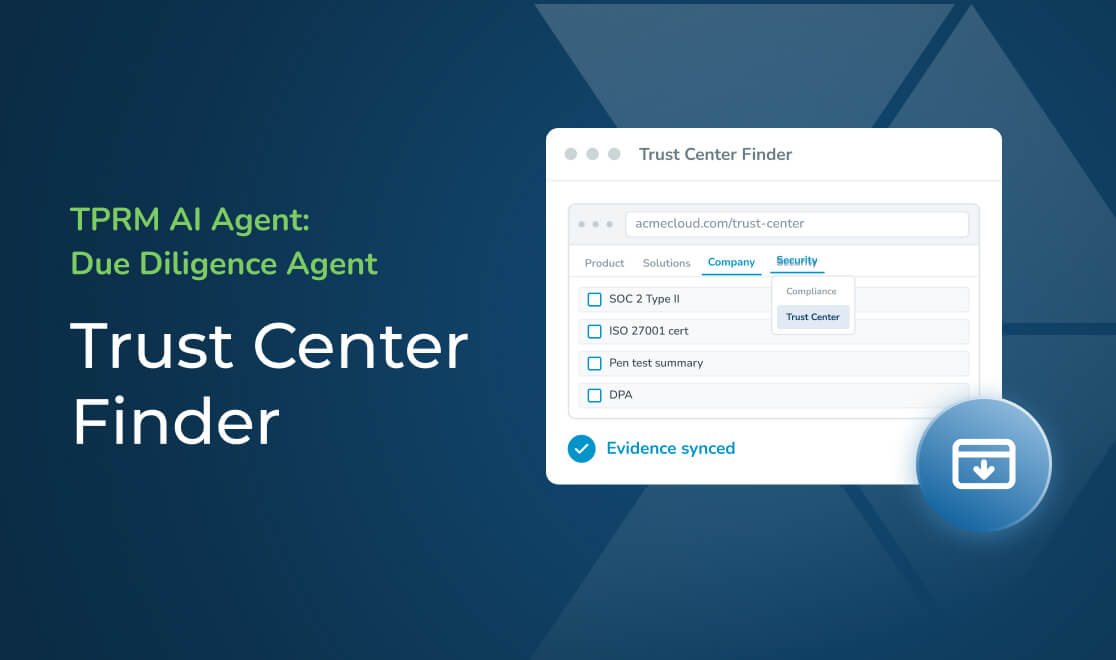
TPRM AI Agent: Trust Center Finder
Teams often request documents that vendors already publish in their trust centers. The resulting email exchanges add days to assessments, create unnecessary questionnaire cycles, and frustrate both the vendor and your internal team.
No results found.